
In the second half of 2025, the fraud rate on instant credit transfers in Italy fell from €45 to €28 for every €100,000 transacted, a reduction of almost 40 per cent, according to the Bank of Italy‘s Report on Fraudulent Payment Transactions. The fall followed the introduction of enhanced fraud prevention measures, among them Verification of Payee (VoP), mandatory for euro-area payment service providers since October 2025 under the EU Instant Payments Regulation.

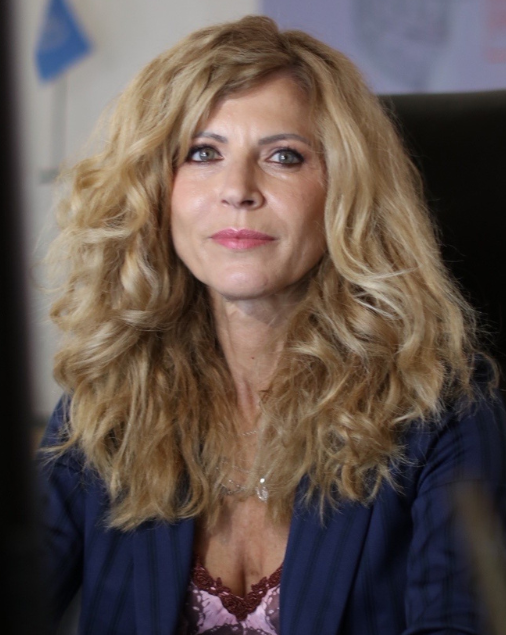
For Liliana Fratini Passi, managing director of CBI, the Italian paytech owned by banks, payment service providers and Poste Italiane, the figures confirm the principle now shaping the company’s security agenda. “This demonstrates the value of identifying and stopping fraudulent transactions before funds leave the account, rather than attempting to intervene once the payment has already been executed,” she tells The Fintech Times.
Fratini Passi has led CBI since 2001, steering it from an interbank association into a Public limited Consortium Company and Benefit Corporation at the centre of Italy’s open banking and open finance infrastructure. “Over the past decade, digital payments have moved from being a convenient alternative to becoming an essential layer of our economy,” she says. That shift has created opportunities for innovation and inclusion, but it has also expanded the surface of risk. Security, she says, is “no longer a back-office requirement: it is a strategic condition for trust”.
Acceleration has changed fraud in both scale and nature. “When money moves instantly, the window to detect and stop fraud becomes much shorter,” she says. “Cyber criminals are not simply doing more of the same; they are adapting their methods, using data, automation, artificial intelligence and social engineering to make scams more targeted and convincing.” Controls applied during or after the payment are no longer sufficient, she argues, because the threat is “not only bigger; it is more dynamic, more sophisticated and often more human-centred”.
A name behind every IBAN
Verification of Payee addresses the point where much of that manipulation lands. Before a payment is authorised, the service checks whether the name entered by the payer matches the beneficiary associated with the IBAN. CBI’s implementation, CBI Name Check, lets payment service providers run the check quickly and securely across domestic and cross-border use cases. “Many fraud cases rely on misdirection: convincing someone to transfer funds to an account that does not belong to the intended recipient,” Fratini Passi explains. Confirming the name behind an IBAN “introduces an important moment of awareness into the payment journey, without adding unnecessary complexity”.
Months into mandatory operation at scale, she draws one lesson above the others. “Verification of Payee works best when it is treated not only as a regulatory obligation, but as a market-wide trust infrastructure,” she says, pointing to interoperability, common standards and clear customer communication as the conditions that keep the check feeling like protection rather than friction. The speed of public acceptance has been the unexpected part. “What has surprised me most is how rapidly VoP has become part of people’s security expectations: a small pause that can prevent errors, expose scams and strengthen confidence in instant payments.”
Request to Pay, often described as one of the most underused instruments in European payments, protects a different moment in the journey. It allows a payee to send a structured payment request that the payer can review and approve in a controlled way. “This contributes to fraud prevention because it reduces ambiguity and gives the payer clearer information before authorising the payment, limiting the risk of errors, impersonation or manipulated instructions,” she says. The same structure smooths the financial value chain, linking invoices, execution and reconciliation, and CBI’s Request to Pay service supports corporates across Italy and the SEPA area with faster collections, lower operational costs and better traceability.
Together, the two services form a layered defence: “one strengthens beneficiary verification, the other improves transparency, control and reconciliation around the payment instruction”. But infrastructure only goes so far. Banks must integrate the tools into clear customer journeys, businesses must keep their data and processes sound, and customers must stay alert to warnings and unusual requests.
That human dimension matters most where criminals now concentrate their effort. “AI, deepfakes and social engineering are powerful because they exploit urgency, trust and emotion rather than only technical vulnerabilities,” Fratini Passi says. Network-level checks can slow manipulation down and surface inconsistencies at the moment a victim is under pressure, but she is clear they cannot solve the problem alone: customer awareness, strong authentication, fraud intelligence sharing and cooperation between providers, authorities and businesses all have to carry part of the load.
Common rules, common language
Cooperation is also where her wider roles come in. Alongside CBI, Fratini Passi serves as vice chair of UN/CEFACT and works within the ISO 20022 standardisation community. “Standards are not abstract technical exercises, but practical tools to improve transparency, interoperability and resilience across markets,” she says. The point is not theoretical: in 2010 CBI registered its Creditor Payment Activation Request messages in the ISO 20022 repository, and those messages now provide the foundation for Request to Pay services.
On the perennial tension between security and convenience, she rejects the framing. The balance “should not be seen as a trade-off, but as a design challenge”, built on what she calls smart friction: checks that appear at the right moment, are easy to understand and carry meaningful information. “I believe the balance will settle around invisible infrastructures and visible trust signals: most of the complexity should remain behind the scenes, while users receive simple, timely and actionable warnings.”
Over the next three to five years, Fratini Passi expects trust, security and resilience to move from individual institutional priorities to shared ecosystem capabilities, governed by common standards and clear responsibilities. CBI’s agenda for that period is set: strengthening CBI Name Check and Request to Pay, supporting interoperability across Europe, and developing secure, scalable solutions for open finance, corporate payments and future digital payment ecosystems. “Ultimately, innovation must make payments not only faster and more convenient, but safer, more transparent and more resilient for everyone.”
The post CBI’s Fratini Passi on Stopping Fraud Before the Money Moves appeared first on The Fintech Times.

